 Free up to 50 domains, no credit card required
One home for every domain you own
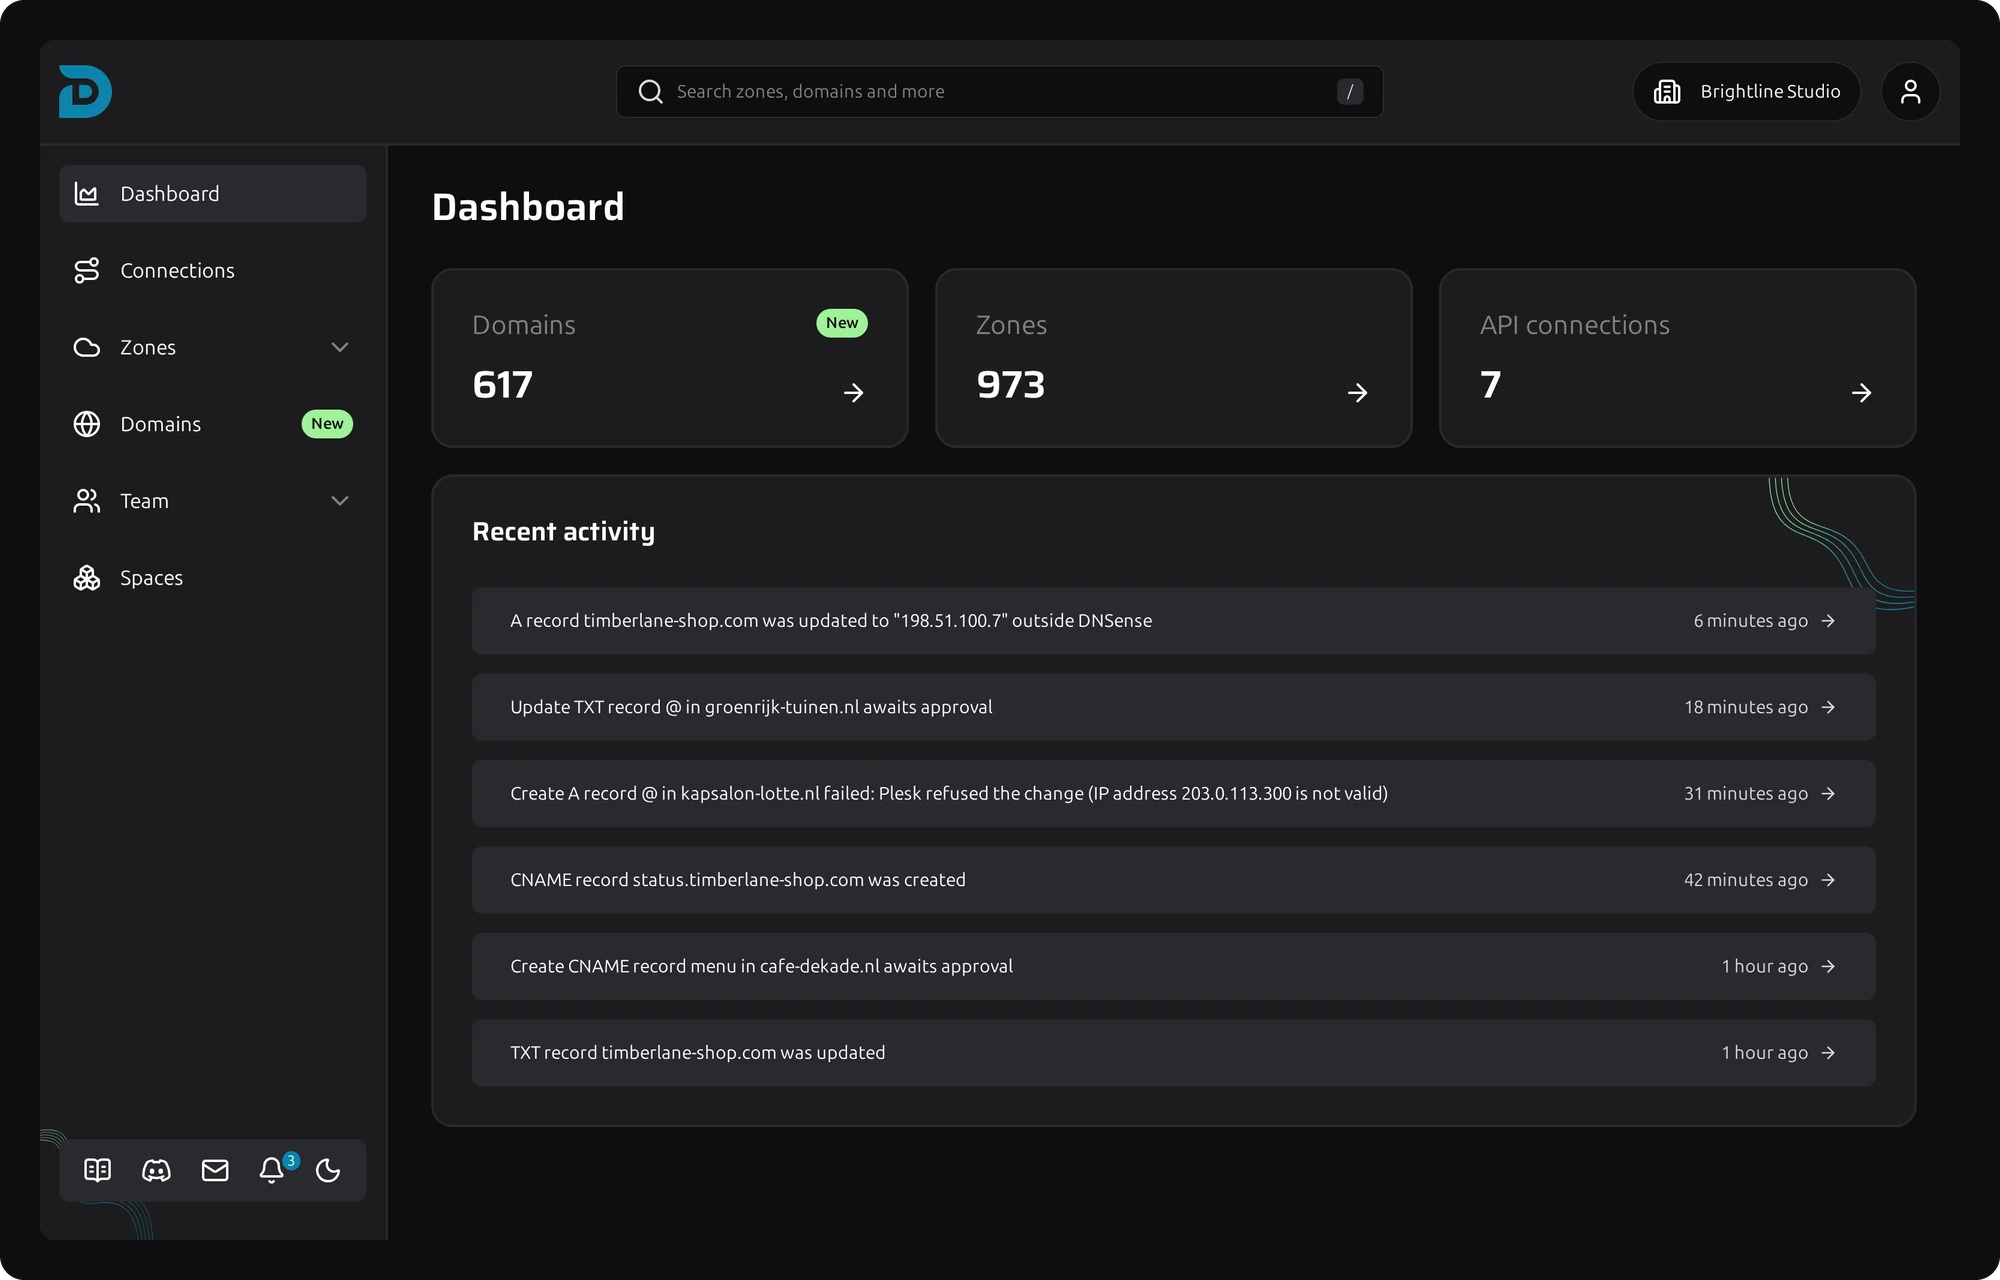
Domains are spread over registrars, hosting panels and Cloudflare accounts. DNSense is the multi-provider DNS management tool that connects to all of them, so you change a record without hunting for the right login, roll out the same setup in one action and undo any mistake in one click. Your domains stay exactly where they are.
Trusted by


Domain management without the mess
Every provider in one interface
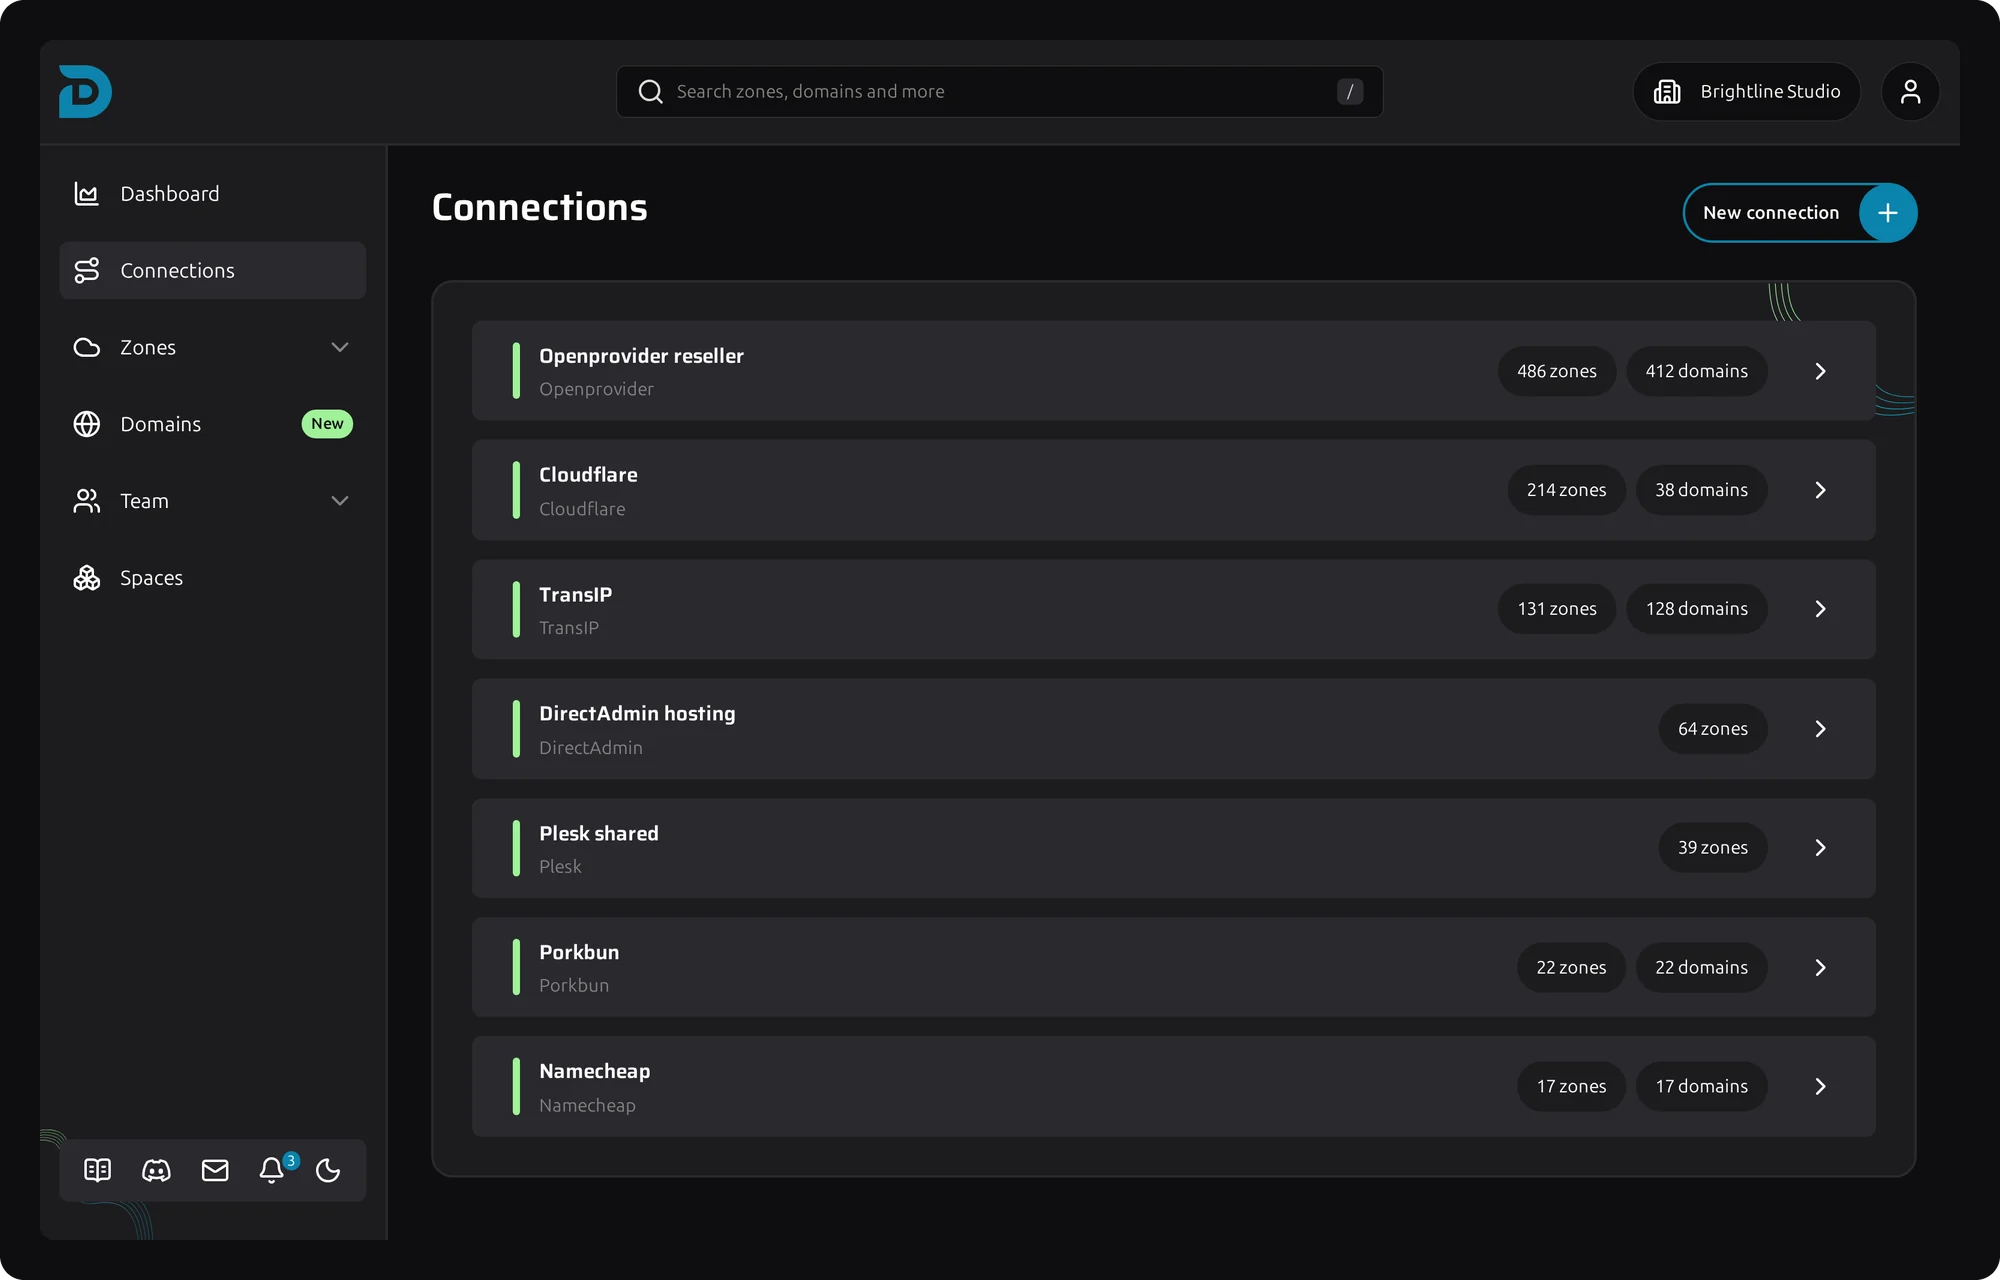
Domains pile up across registrars and hosters over the years. DNSense connects to Openprovider, TransIP, Cloudflare, DirectAdmin and the rest, and shows every domain and zone in one overview. You know where each domain lives before you open it.
Every change, one click from undone
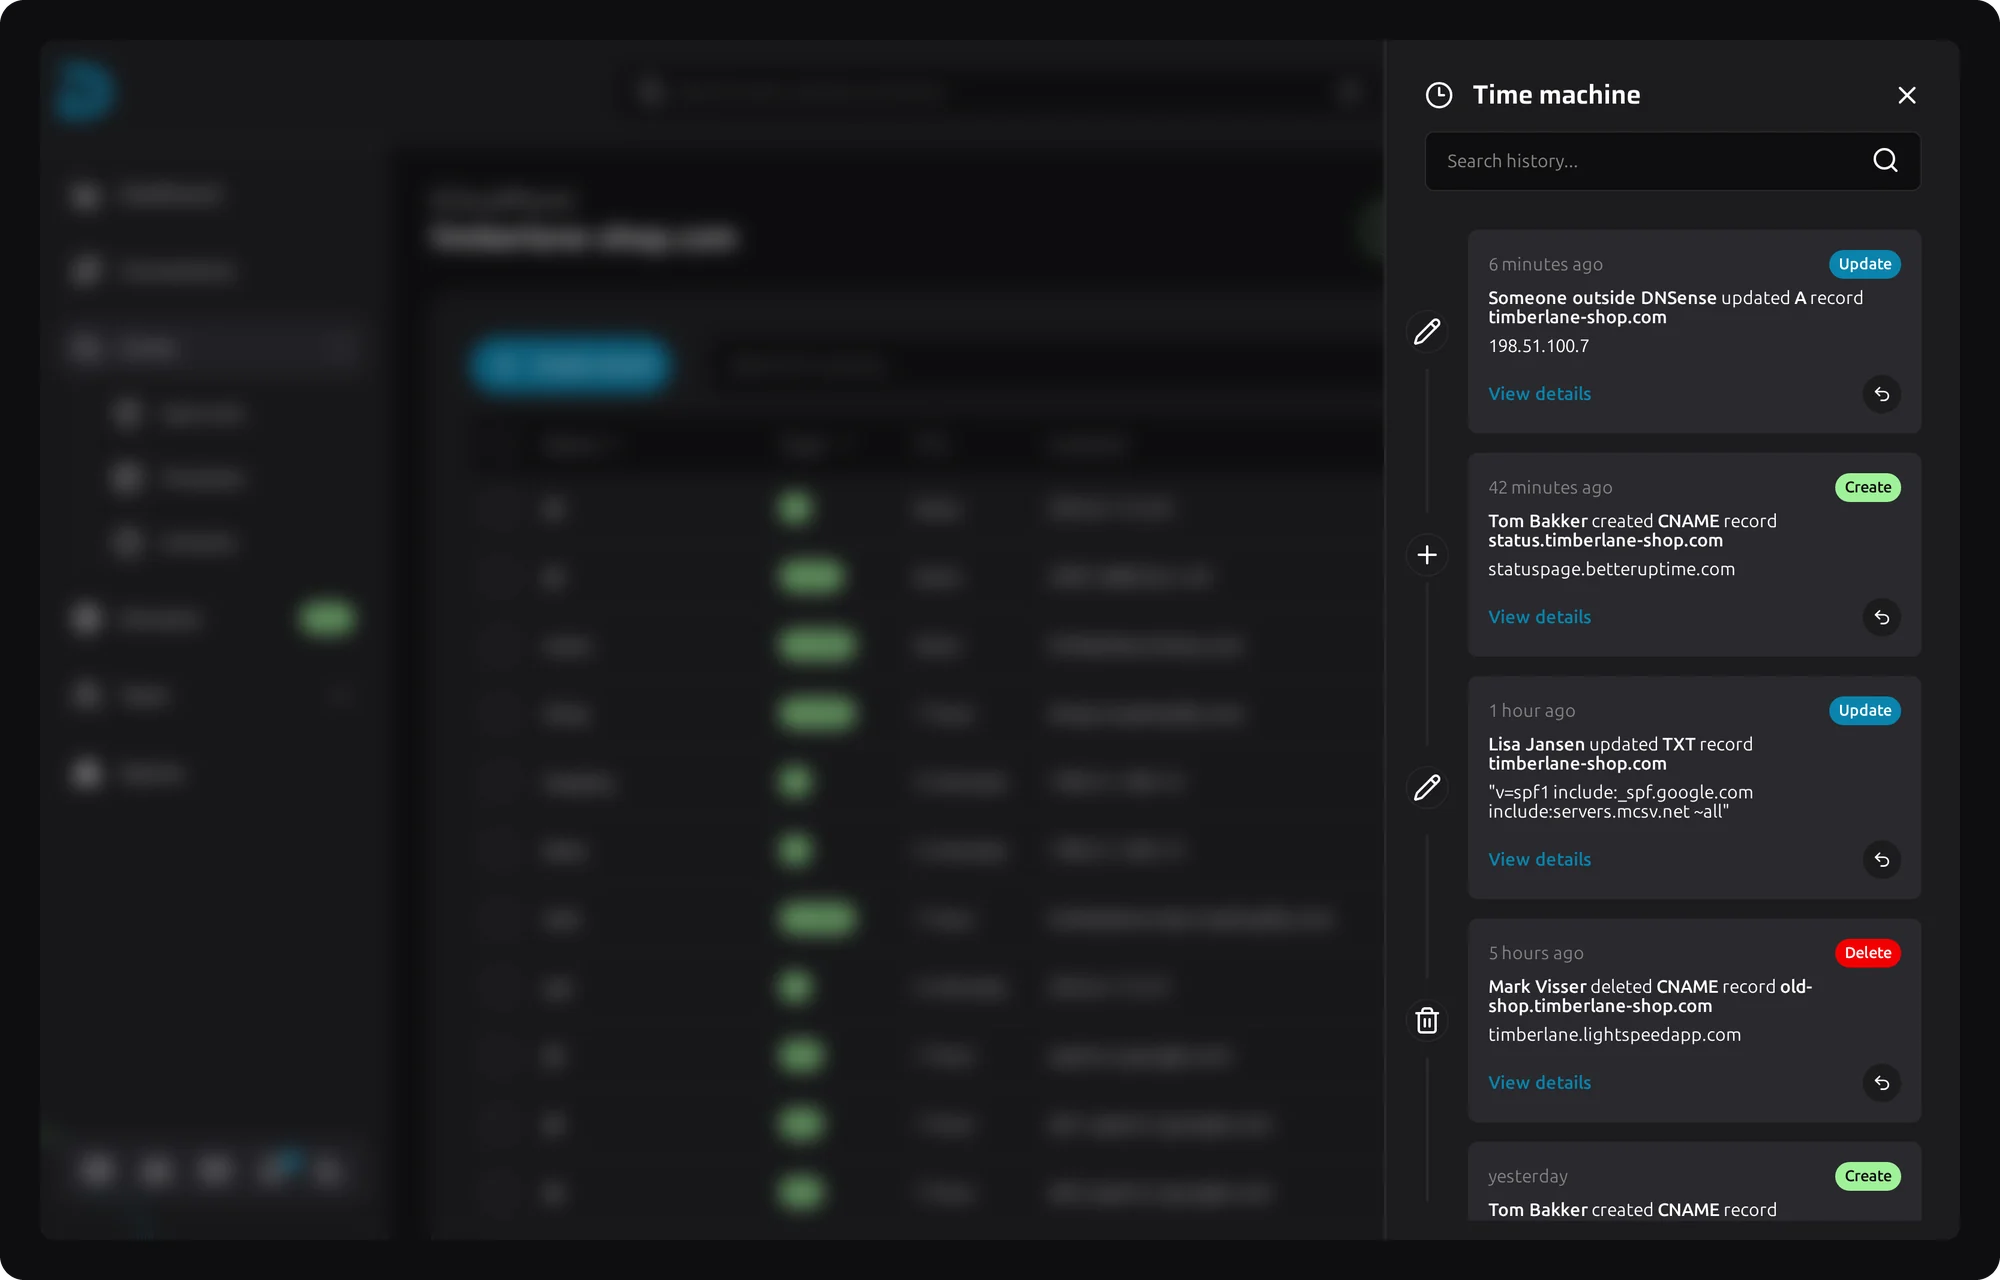
Time machine records every DNS change with the record before and after, also the ones made directly at the provider. Find the change that broke mail and put it back from the same screen.
Access without sharing credentials
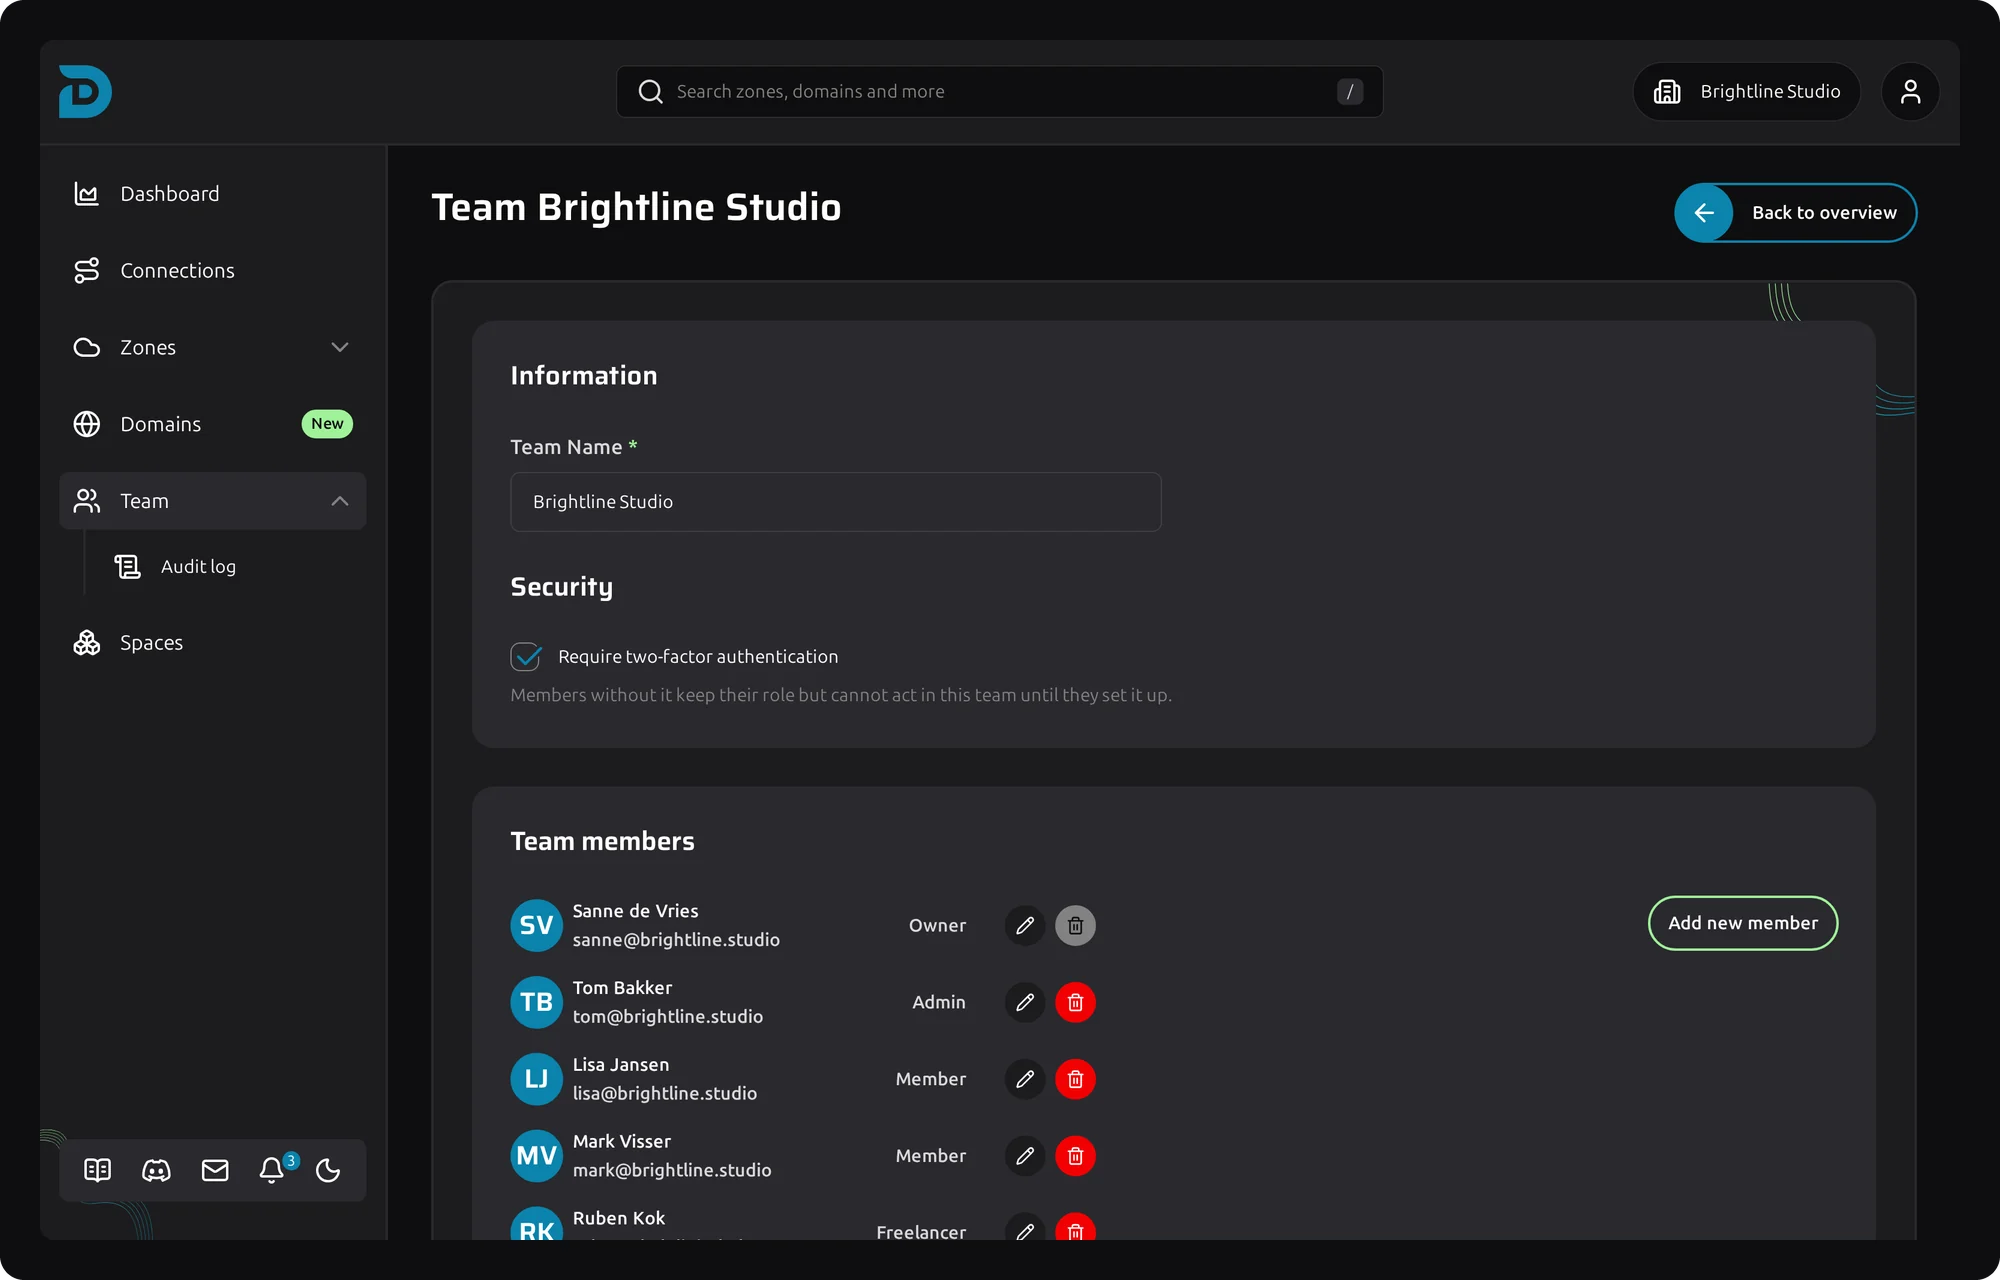
Colleagues, freelancers and external parties get exactly the access they need. Changes can wait for approval before they go live, two-factor can be required for the whole team and every action is in an audit log nobody can edit.
 Integrations
Integrated with well-known domain and DNS providers
DNSense connects to the registrars and DNS hosts most teams use. Connect as many accounts as you have, on every plan. Missing your provider? Tell us and we add it, free of charge.

Cloudflare
(opens in a new tab)'/%3e%3cg%3e%3cg%3e%3cpath%20class='cls-2'%20d='M67.095,43.356a30.81,30.81,0,0,0-8.487-3.174,9.914,9.914,0,0,0,.991,9.947A19.594,19.594,0,0,1,67.095,43.356Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-2'%20d='M92.358,50.129a9.914,9.914,0,0,0,.991-9.947,30.81,30.81,0,0,0-8.487,3.174A19.594,19.594,0,0,1,92.358,50.129Z'%20transform='translate(-42.146%20-23.648)'/%3e%3c/g%3e%3cg%3e%3cpath%20class='cls-2'%20d='M80.515,54.652a1.075,1.075,0,0,0-.883,1.69h0a3.137,3.137,0,0,0,1.651,1.172,2.95,2.95,0,0,0,.347-1.39,2.876,2.876,0,0,0-.048-.5A1.073,1.073,0,0,0,80.515,54.652Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-2'%20d='M75.312,42.469c-9.9.352-17.6,8.789-17.6,18.7V71.436a3.343,3.343,0,0,0,6.686,0V68.755H87.562v2.681a3.343,3.343,0,0,0,6.686,0V60.727A18.27,18.27,0,0,0,75.312,42.469ZM85.737,56.881a4.35,4.35,0,0,1-2.615,2.052,4.338,4.338,0,0,1-3.859,2.358c-.182,0-.4-.029-.535-.037a1.1,1.1,0,0,1-1.07-1.082,1.083,1.083,0,0,1,1.07-1.082h0a2.953,2.953,0,0,0,1.414-.4,4.363,4.363,0,0,1-1.626-1.3,2.6,2.6,0,1,1,4.085-3.2,4.308,4.308,0,0,1,1,2.763c0,.119-.008.236-.018.352a3.144,3.144,0,0,0,1.169-1.028.577.577,0,0,1,.98.608Z'%20transform='translate(-42.146%20-23.648)'/%3e%3c/g%3e%3c/g%3e%3cg%3e%3cpath%20class='cls-3'%20d='M128.037,44.608h4.453V46.76a17.754,17.754,0,0,1-.1,1.851h.1s2.151-4.6,8.506-4.6c6.8,0,11.107,5.4,11.107,13.259,0,8.056-4.853,13.259-11.458,13.259a8.811,8.811,0,0,1-7.755-4.153h-.1s.1.9.1,2.2V79.932h-4.853ZM139.9,66.373c4,0,7.3-3.3,7.3-9.056,0-5.5-2.952-9.056-7.155-9.056-3.8,0-7.3,2.652-7.3,9.106C132.74,61.87,135.242,66.373,139.9,66.373Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-3'%20d='M170.86,44.008c7.555,0,13.659,5.554,13.659,13.209,0,7.705-6.1,13.309-13.659,13.309S157.2,64.922,157.2,57.217C157.2,49.561,163.3,44.008,170.86,44.008Zm0,22.315a8.746,8.746,0,0,0,8.706-9.106,8.711,8.711,0,1,0-17.412,0A8.776,8.776,0,0,0,170.86,66.323Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-3'%20d='M191.269,44.608h4.7v4.4a18.152,18.152,0,0,1-.1,1.9h.1c1.15-3.7,4.1-6.6,8.005-6.6a8.6,8.6,0,0,1,1.25.1v4.8a7,7,0,0,0-1.4-.15c-3.1,0-5.954,2.2-7.1,5.954a15.389,15.389,0,0,0-.6,4.553V69.925h-4.853Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-3'%20d='M211.028,34.6h4.853V53.914h3.552l6.9-9.306h5.5l-8.406,11.157v.1l9.356,14.06h-5.654l-7.605-11.908h-3.652V69.925h-4.853Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-3'%20d='M238.342,34.6H243.2V46.159c0,1.251-.1,2.152-.1,2.152h.1a8.941,8.941,0,0,1,8.105-4.3c6.8,0,11.107,5.4,11.107,13.259,0,8.056-4.853,13.259-11.508,13.259a9.1,9.1,0,0,1-7.955-4.353h-.1a16.975,16.975,0,0,1,.1,1.9v1.851h-4.6ZM250.2,66.373c4,0,7.3-3.3,7.3-9.056,0-5.5-2.952-9.056-7.155-9.056-3.8,0-7.3,2.652-7.3,9.106C243.045,61.87,245.4,66.373,250.2,66.373Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-3'%20d='M269.007,44.608h4.854v15.11c0,3.5.7,6.3,4.753,6.3,5.154,0,8.206-4.553,8.206-9.556V44.608h4.854V69.925h-4.7V66.573a16.581,16.581,0,0,1,.1-1.852h-.1a10.21,10.21,0,0,1-9.307,5.8c-5.7,0-8.656-3-8.656-9.707Z'%20transform='translate(-42.146%20-23.648)'/%3e%3cpath%20class='cls-3'%20d='M300.272,44.608h4.7V47.96a17.758,17.758,0,0,1-.1,1.852h.1a10.305,10.305,0,0,1,9.506-5.8c5.954,0,8.706,3.252,8.706,9.707V69.925h-4.853V54.815c0-3.552-.75-6.354-4.8-6.354a8.291,8.291,0,0,0-8.005,6.2,11.98,11.98,0,0,0-.4,3.4V69.925h-4.853Z'%20transform='translate(-42.146%20-23.648)'/%3e%3c/g%3e%3c/g%3e%3c/svg%3e)
Porkbun
(opens in a new tab)
Hetzner
(opens in a new tab)
TransIP
(opens in a new tab)
GoDaddy
(opens in a new tab)
OpenProvider
(opens in a new tab)
NameCheap
(opens in a new tab)
Versio
(opens in a new tab)
cPanel
(opens in a new tab)
DirectAdmin
(opens in a new tab)
Plesk
(opens in a new tab)
PowerDNS
(opens in a new tab)
AWS Route 53
(opens in a new tab)
NextName
(opens in a new tab)Hand over the manual work
Domains and DNS zones
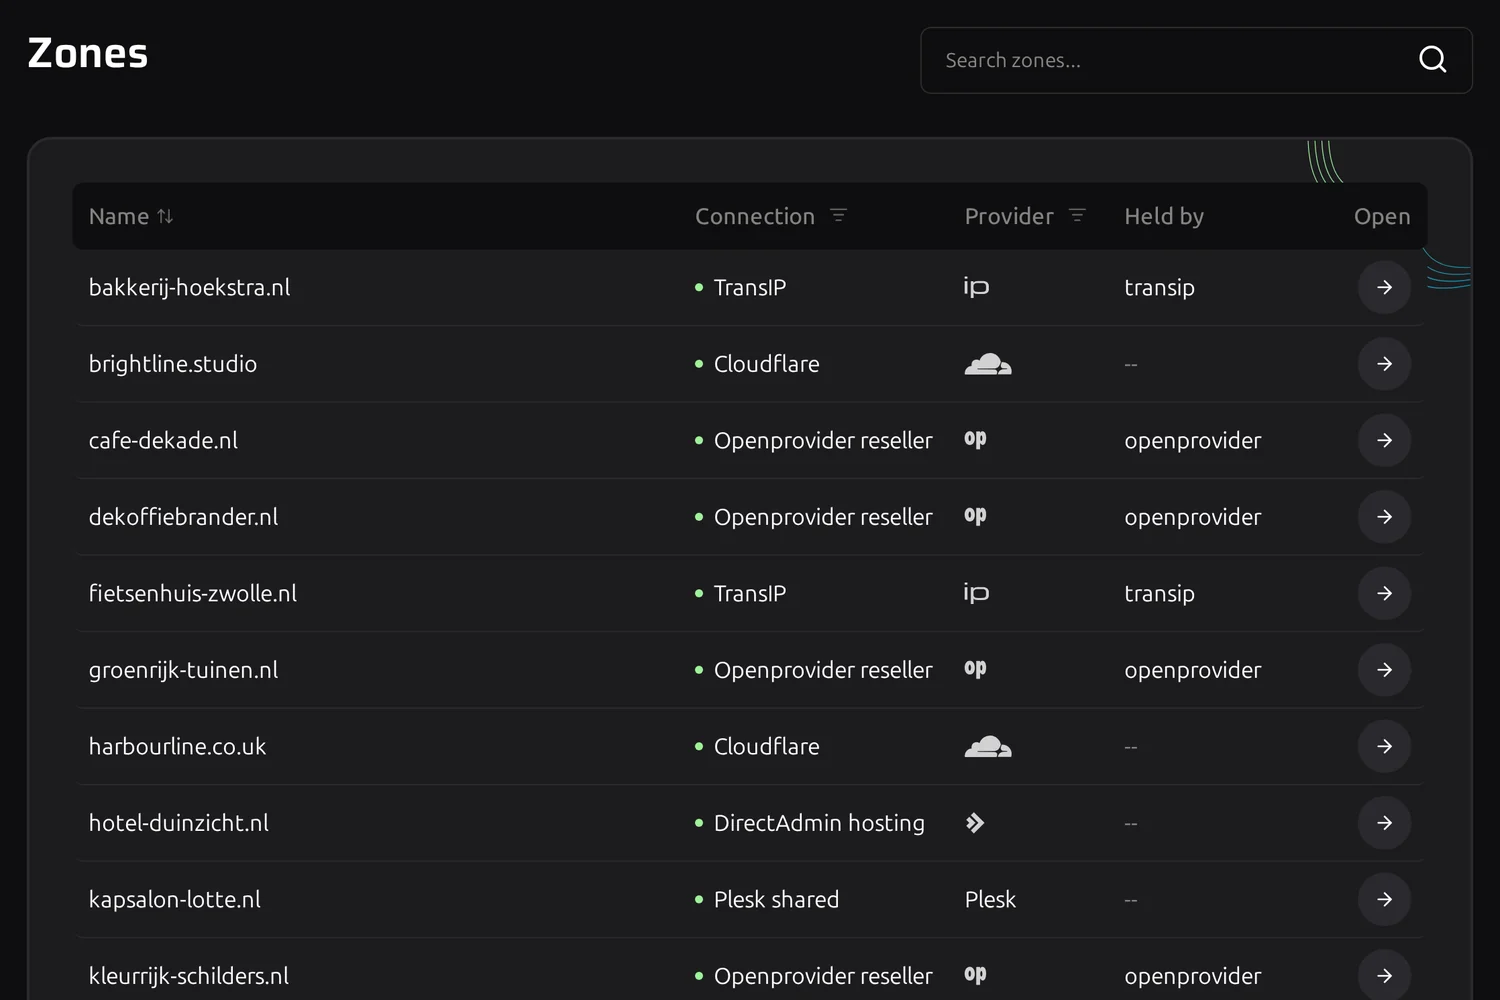
Every domain and DNS zone sits in one overview, with the connection it came from. Edit any zone from here and DNSense pushes the change to the provider that hosts it. Press / on any screen to search zones, domains and team members at once.
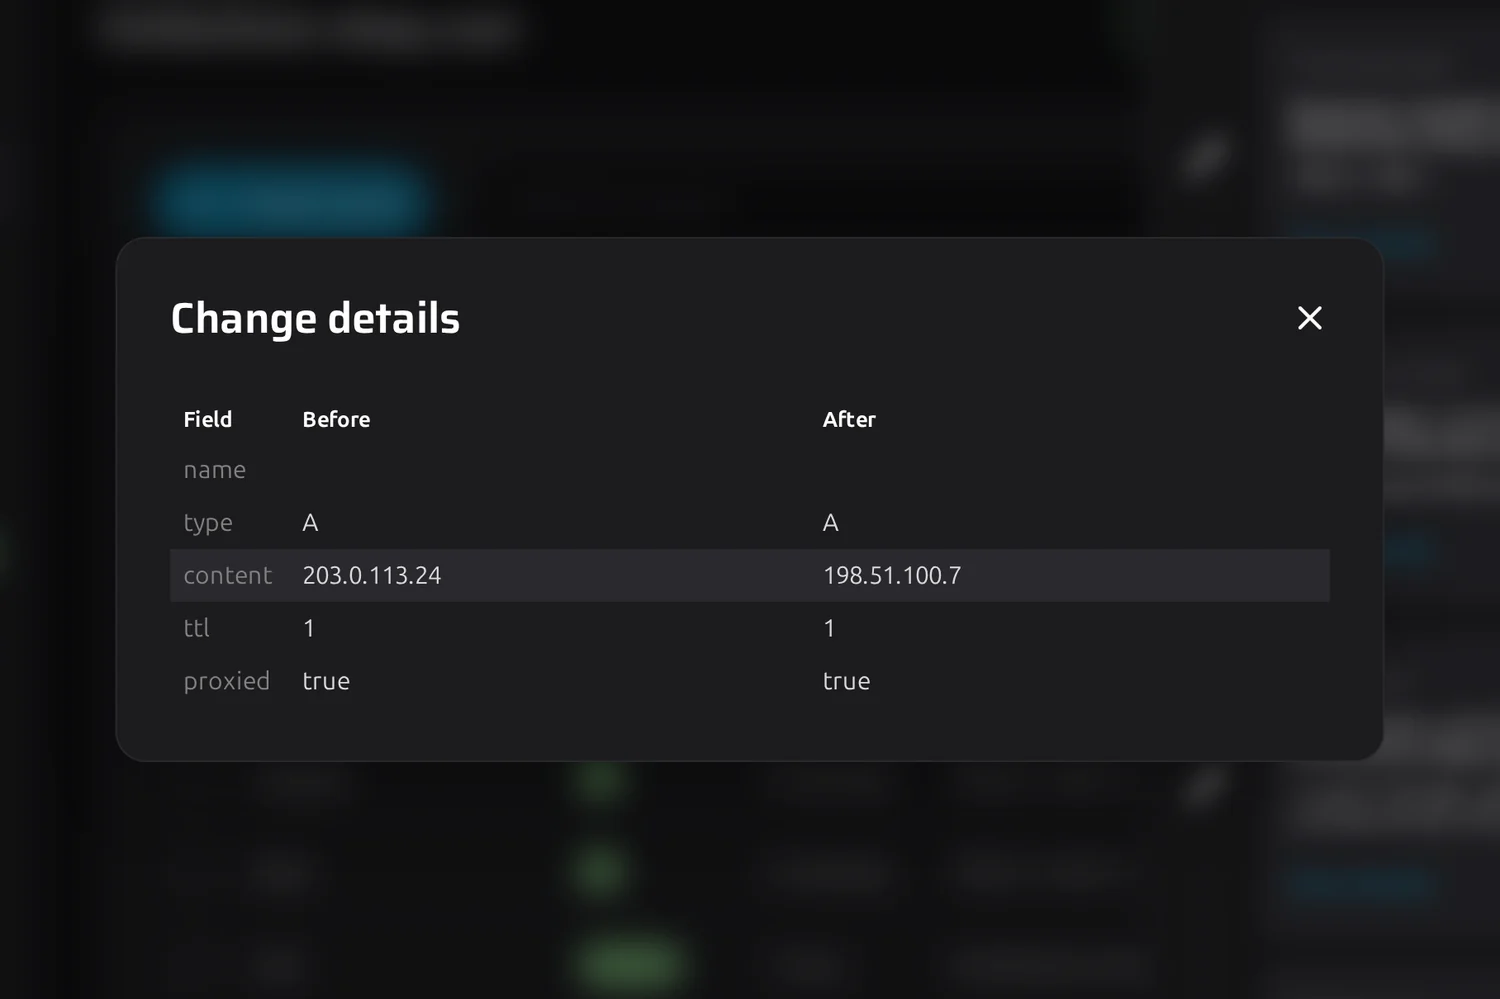
Time machine
Every change is recorded with what changed, when and who did it, including changes made outside DNSense. Open an entry to compare the record before and after, and revert it in one click.
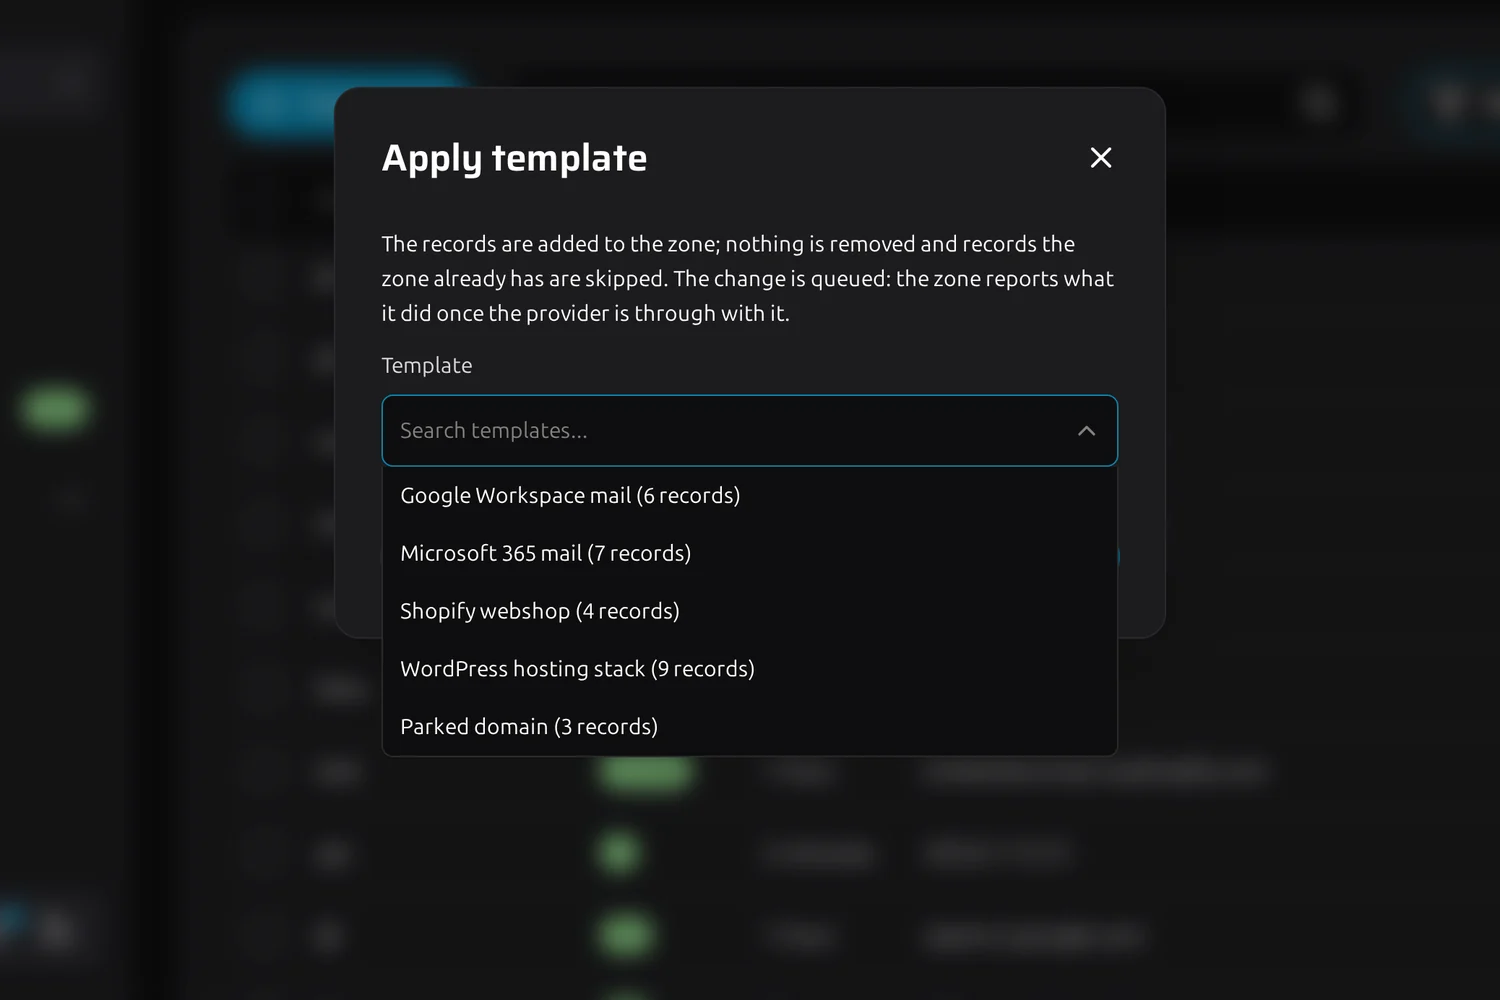
DNS templates
Save your Google Workspace, Microsoft 365 or hosting setup once and apply it to the next zone in one action. Records the zone already has are skipped, and BIND zone files import too.
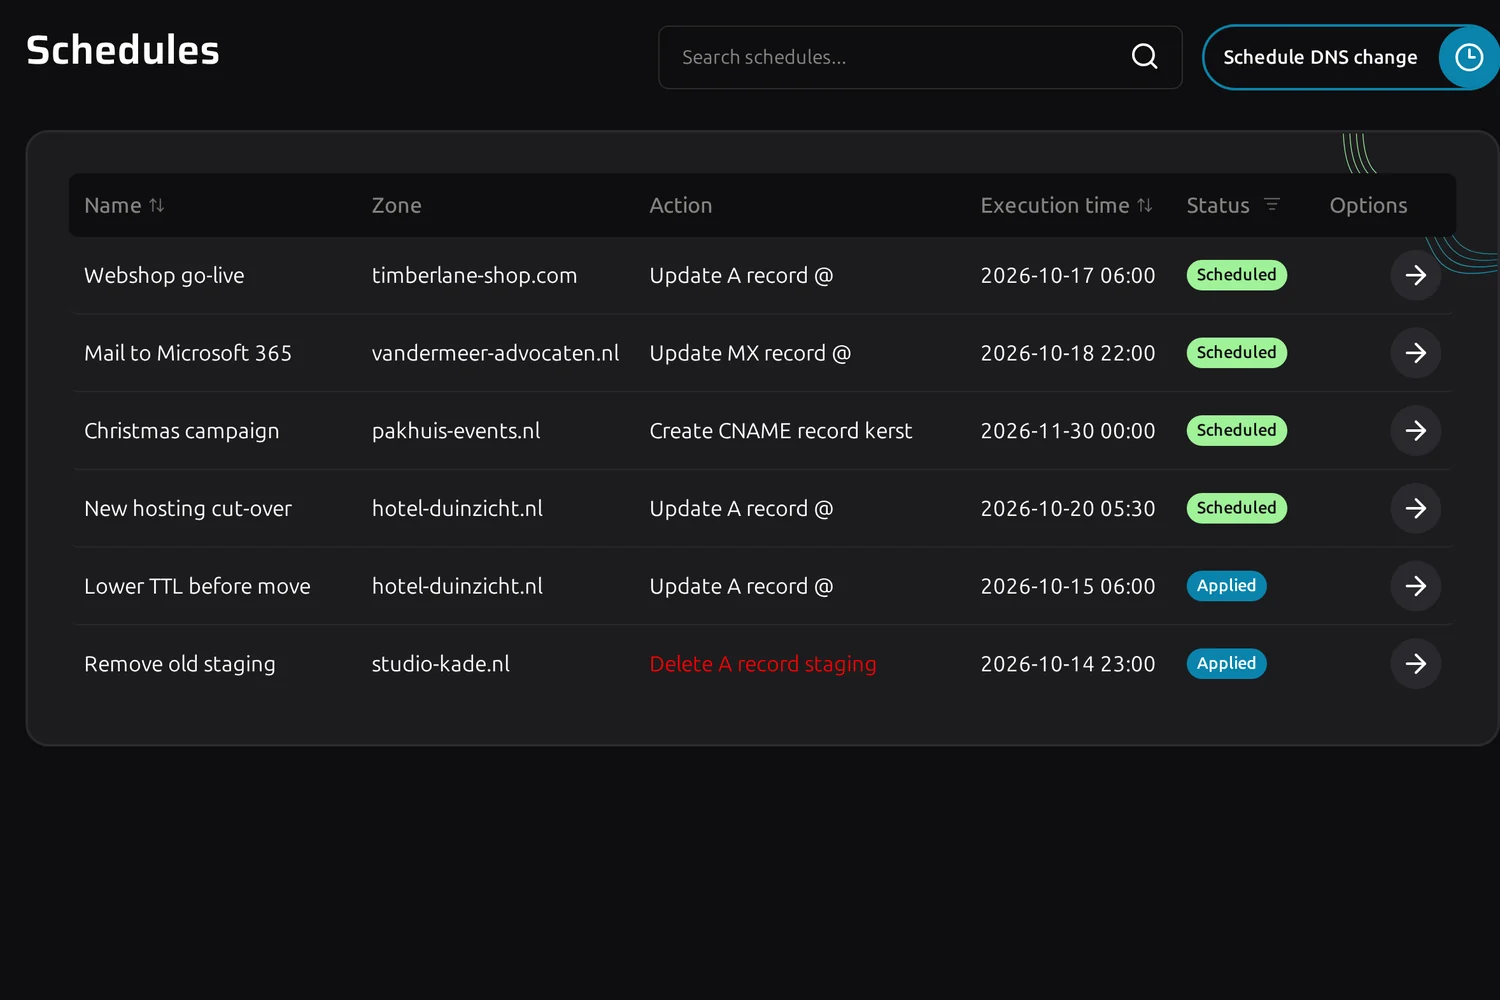
Switcher
Prepare a record change by day and pick the minute it goes live. Switcher runs it at 06:00 on Saturday while nobody is awake, and the result shows up next to the schedule and in Time machine.
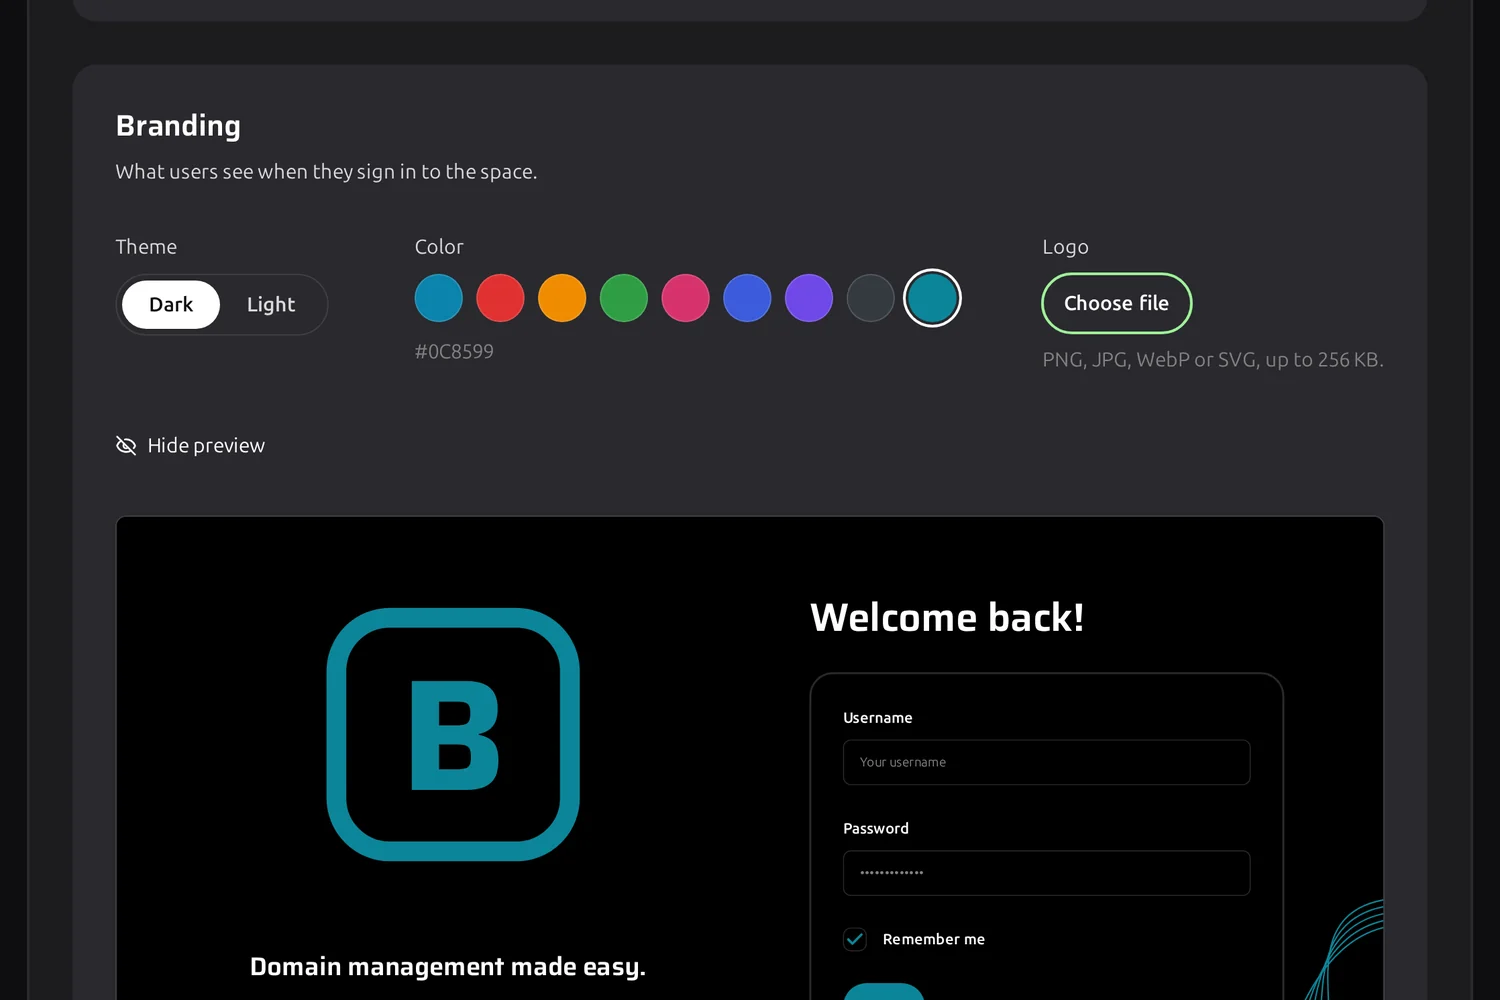
Spaces
Give external parties their own zones in a Space on your own address, with your logo and colours. No registrar logins handed over, no view of your other zones. White-label is included in every plan.
Great minds think alike
See why others are using DNSense to manage their DNS and domains
Thanks to DNSense, we no longer have to worry about keeping track of our clients' DNS records and domain registrations. Now everything is easily managed in one place.
Our clients' domains used to be spread over five different accounts. Now I manage all of them in one place, and when someone breaks a record I put it back in one click.
Many colleagues work on our customers' DNS every day. The DNSense audit log shows exactly who changed what and when, and nobody can edit or remove an entry.
 Security Practices
Your data is in safe hands
Provider credentials and API tokens are encrypted before they are stored, which keeps them unreadable without our application key. All traffic to DNSense runs over HTTPS, and personal data is handled under the GDPR. Access to the production database is limited to one authorized person, and backups run twice a day.
DNSense follows the GDPR rules on collecting, storing, deleting and processing personal data of European Union citizens. Our GDPR statement and privacy policy list exactly what we store and why.
Provider credentials, API tokens and other sensitive fields are stored encrypted, which leaves them unreadable without the application specific key. Only HTTPS requests to our domain are accepted, on LetsEncrypt and Cloudflare certificates with an A+ rating from SSL Labs.
The audit log keeps a record of who did what and when, and nobody can edit or delete an entry, not even the owner. Changes made at your provider instead of in DNSense are caught by Time machine, so nothing happens to your domains unseen.
Access to the production database is restricted to a single authorized person. Backups run twice daily, and we raise that frequency as the amount of data grows.